Push Left on the Attack Timeline
Practitioner POV: Watch Kirk and Paul walk through a live credential access alert to uncover the full attack context in under 15 minutes.
Follow the evidence, not the red string.
Every analyst knows the drill. A process alert fires, and then the real work starts: checking three other consoles for related network activity or sensitive file access.
So, how do you get from a single alert to the full story without spending the rest of the day tied up in red string?
Join Kirk Hasty and Paul Miller for a live credential access scenario involving LSASS access via comsvcs.dll. Using Symantec CBX’s Targeted Attack Analytics, they’ll surface suspicious activity; group related endpoint, network, and data security events in one place; and show you how to do the same.
Follow the evidence from alert to investigation to uncover lateral movement, the network connection, and whether a sensitive file was touched.
No console-hopping or manual correlation. Just the context you need in one place.
In this webinar, you’ll learn how to:
✔️ Recognize suspicious LSASS credential access
✔️ Trace the process and command line behind it
✔️ Connect endpoint, network, and data activity
✔️ Cut the time to investigate and remediate attacks
✔️ Report findings faster with full context
The Speakers
Join Broadcom’s Kirk Hasty and Paul Miller for a live walkthrough of a common attacker technique.
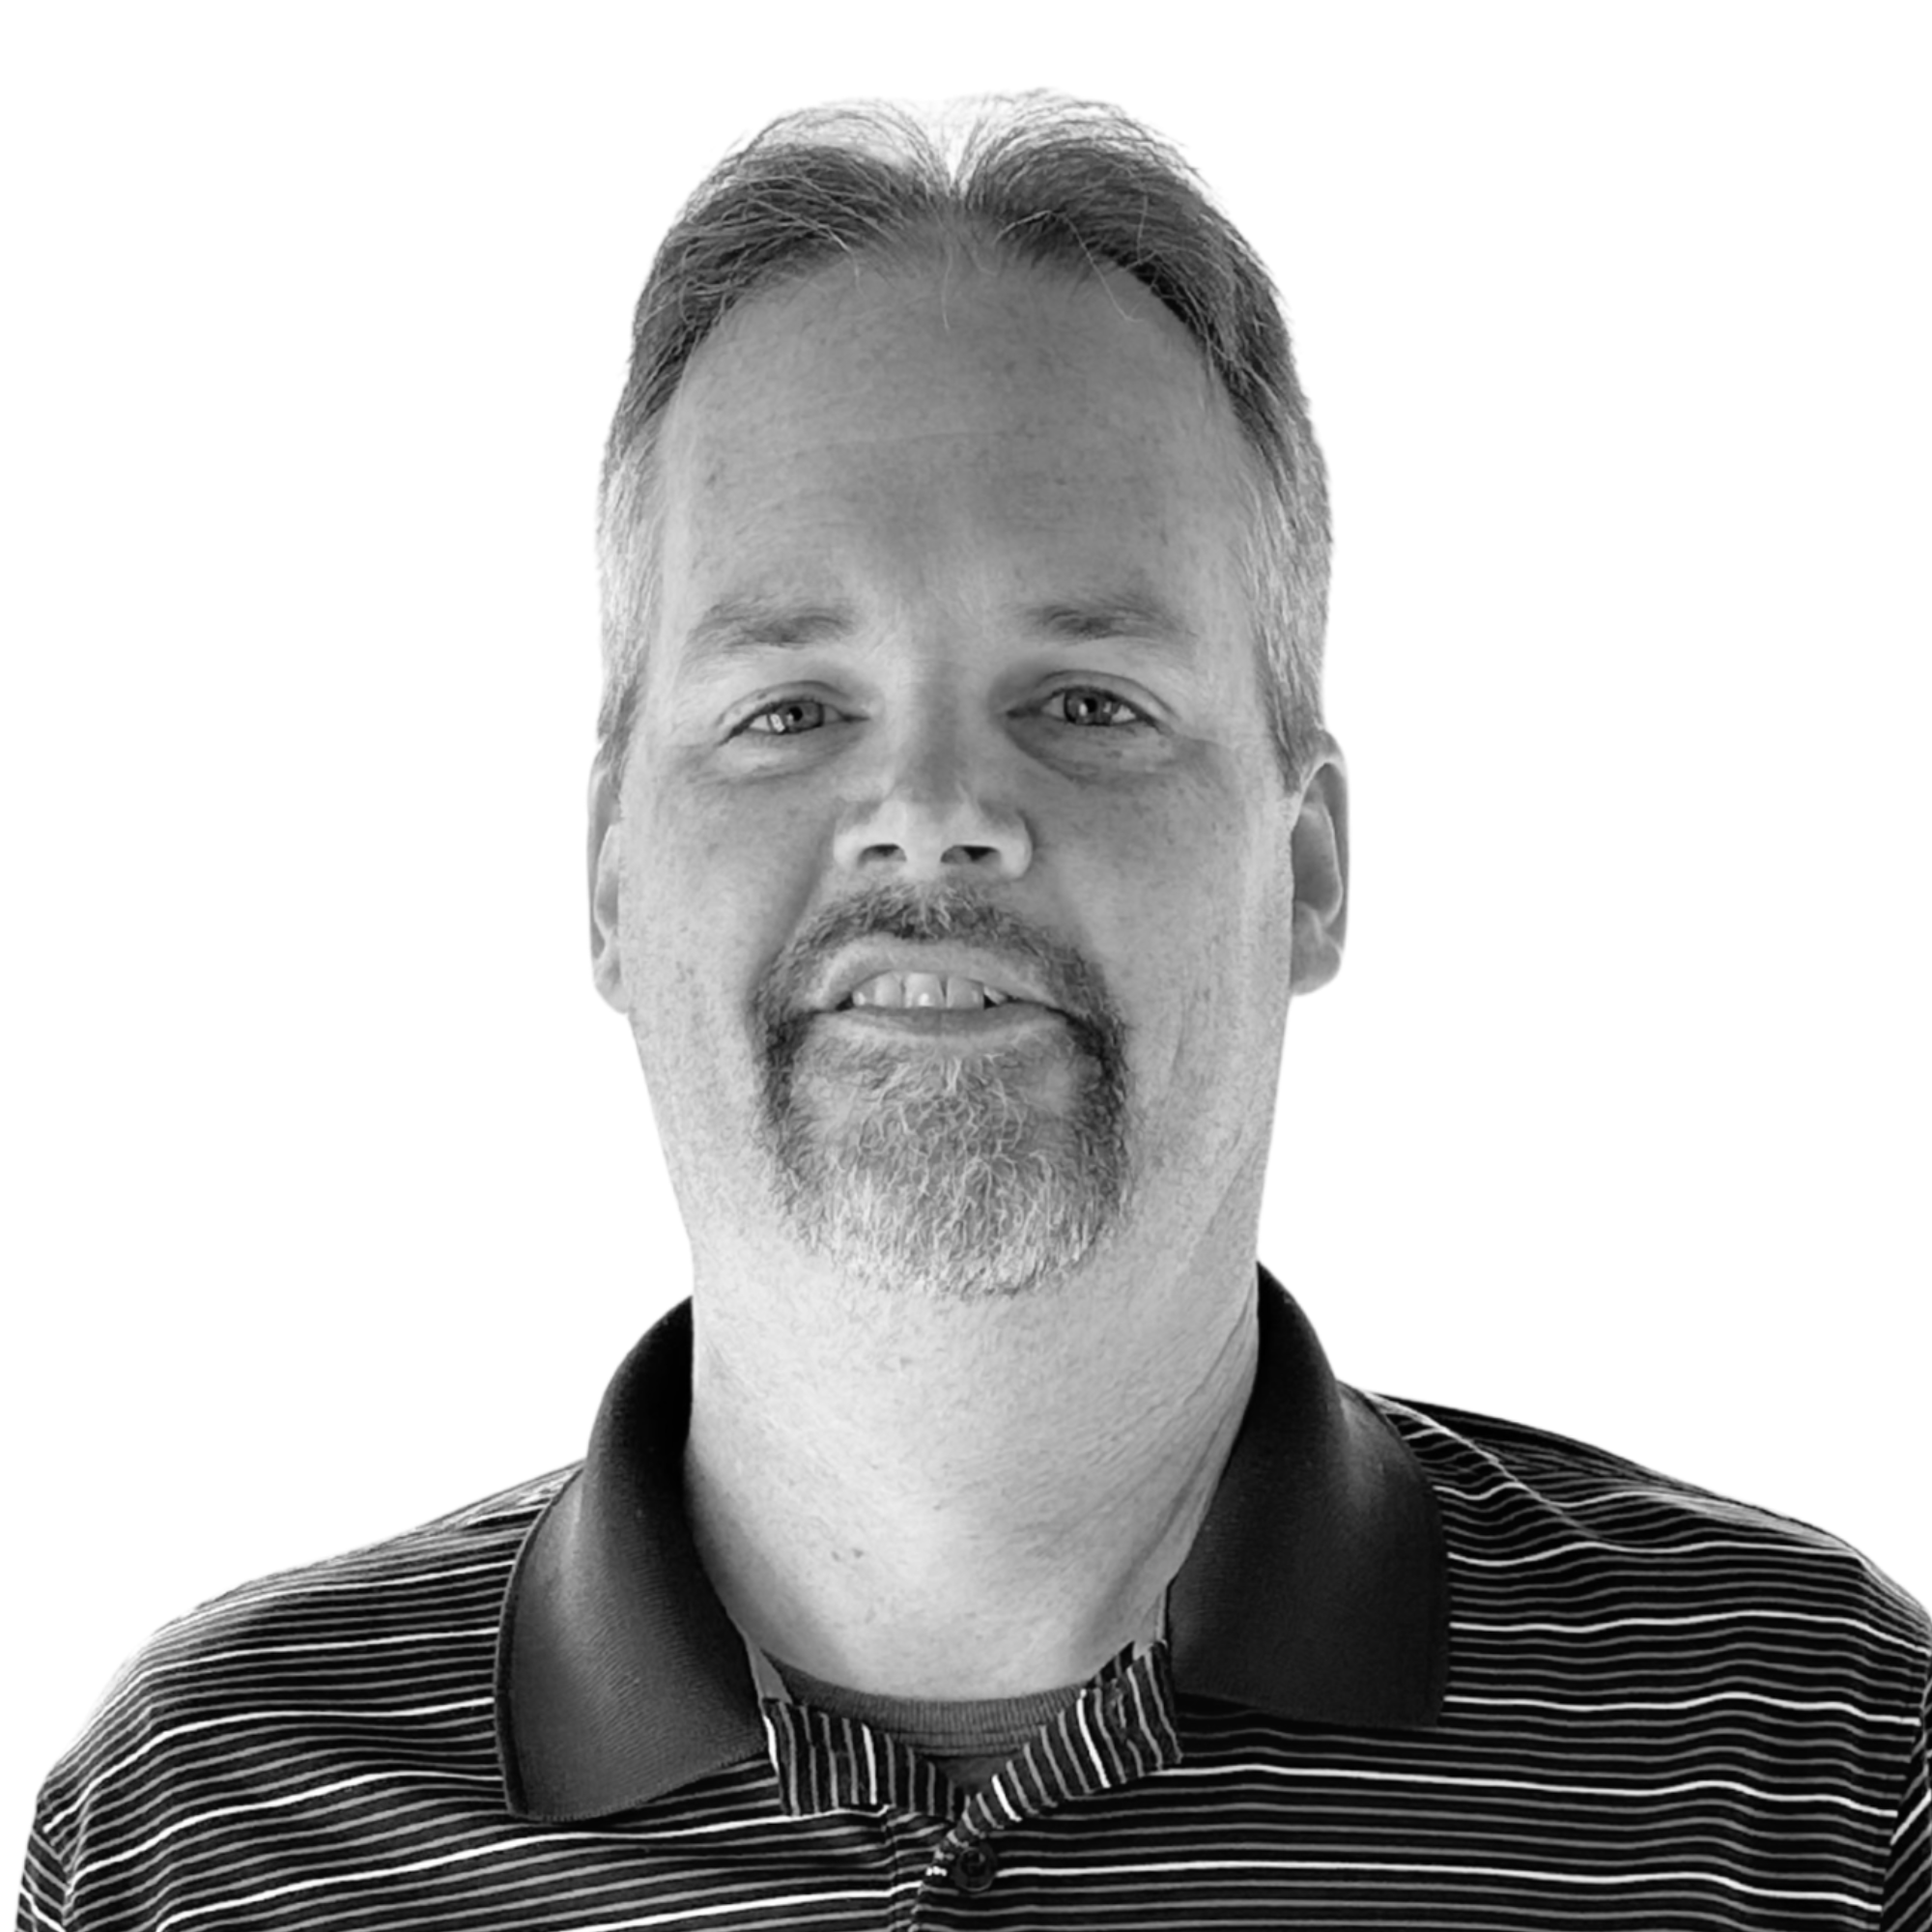
Kirk Hasty
Technical Product Engineer
Enterprise Security Group, Broadcom
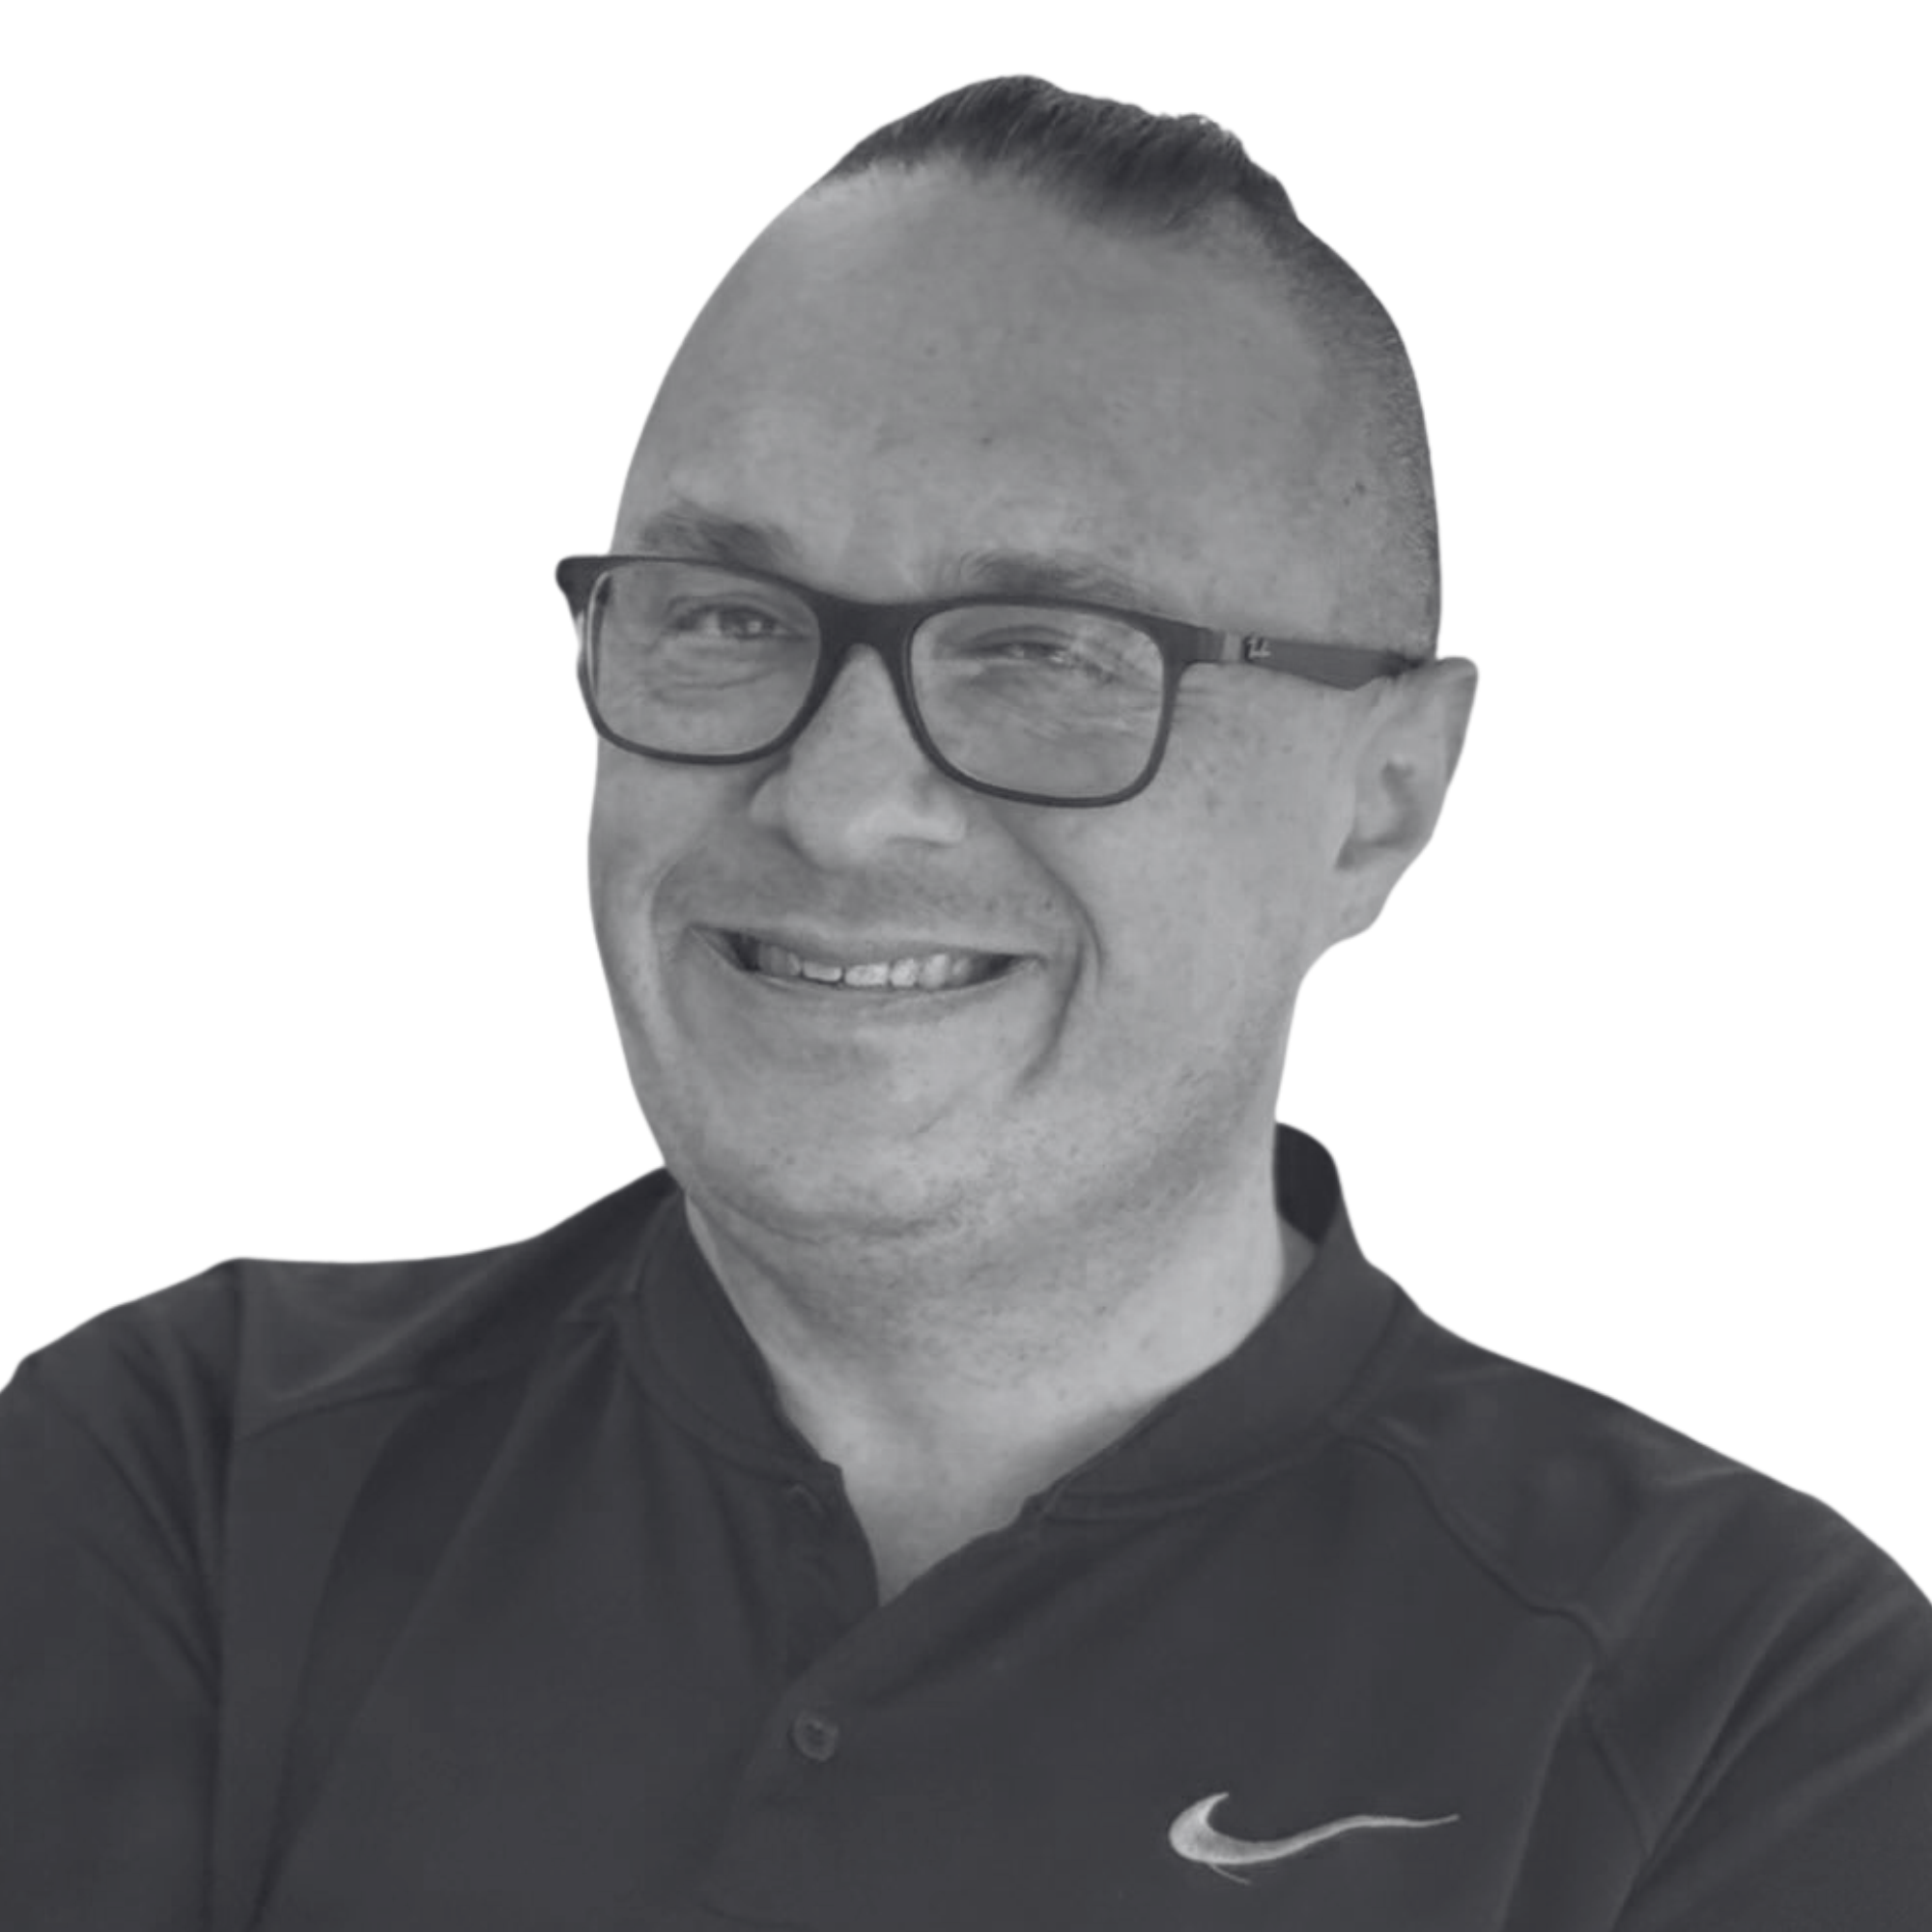
Paul Miller
Cybersecurity Strategist
Enterprise Security Group, Broadcom
Register Now
November 18, 2026 | 1:00 PM ET
In this webinar, you’ll learn how to:
✔️ Recognize suspicious LSASS credential access
✔️ Trace the process and command line behind it
✔️ Connect endpoint, network, and data activity
✔️ Cut the time to investigate and remediate attacks
✔️ Report findings faster with full context